Sophisticated Cyber Campaign Targets Citrix NetScaler Appliances via Critical Memory Overflow Vulnerability

Unknown threat actors have launched a highly coordinated and technically advanced campaign exploiting a critical security flaw in Citrix NetScaler ADC and NetScaler Gateway appliances, impacting a wide array of organizations across North America and Europe. The breach, which came to light in September 2026, has compromised entities spanning the government, financial services, technology, education, and legal sectors. Security researchers from Mandiant Consulting and the Google Threat Intelligence Group (GTIG) have identified the primary vector as CVE-2026-88772, a high-severity memory overflow vulnerability that permits unauthenticated remote code execution with root-level privileges.
The Technical Anatomy of the Breach
At the core of the compromise is CVE-2026-88772, a vulnerability assigned a staggering CVSS score of 9.5. According to analysis provided by watchTowr Labs and confirmed by Google, the flaw resides within the Datagram Transport Layer Security (DTLS) protocol handling of the NetScaler Packet Processing Engine (NSPPE). The vulnerability is triggered during the initial pre-authentication cryptographic handshake. By transmitting specially malformed or fragmented record headers, an attacker can induce heap memory boundary corruption within the packet engine.
This corruption allows the adversary to divert the control flow, executing arbitrary shellcode directly on the underlying FreeBSD operating system. Because this execution occurs at the root level, the attacker gains near-total control over the appliance. This bypasses traditional security perimeters, as the NetScaler is typically positioned at the network edge, acting as a gateway that sits outside the visibility of most endpoint detection and response (EDR) solutions.
Sophisticated Post-Exploitation Tooling
Following the successful initial compromise, the threat actors have demonstrated a sophisticated approach to maintaining persistence and obfuscating their presence. The primary post-exploitation toolkit involves two newly identified components: a PHP-based web shell dubbed WHIPSHOT and a companion Python-based tunneler known as SLAPSHOT.
WHIPSHOT is notable for its stealth capabilities. Rather than utilizing standard, easily detectable command-and-control (C2) patterns, it embeds Base64-encoded instructions directly within native HTTP headers. This allows the attackers to issue commands to the compromised appliance without triggering traditional network traffic alarms.

Once the foothold is established, the attackers utilize SLAPSHOT to create a bridge into the internal network. SLAPSHOT functions as a proxy, allowing the threat actors to tunnel traffic into the internal infrastructure of the victim organization. This secondary layer of the attack is specifically designed for reconnaissance and credential harvesting, enabling the adversary to move laterally from the edge device into the core network environment.
Deployment and Concealment Strategies
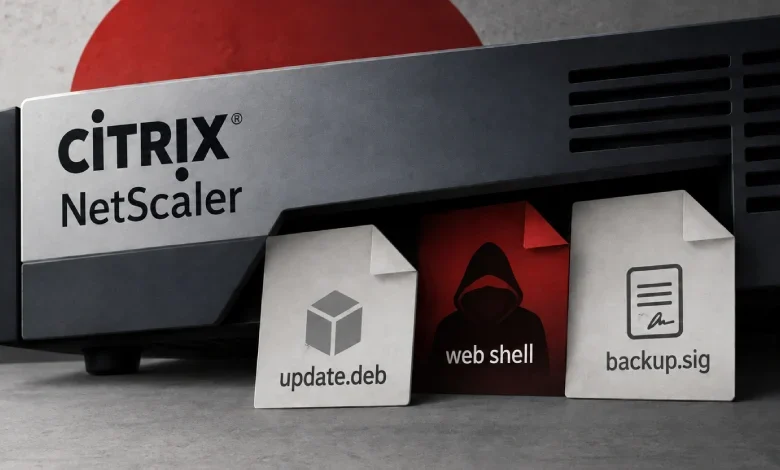
The deployment process for these tools is equally calculated. The attackers modify the target’s httpd.conf files to alter how the server handles specific file types. By configuring the system to interpret .deb (Debian software package) or .sig (signature) files as PHP scripts, the threat actors can store their malicious code in plain sight, disguised as innocuous system or image files.
In several instances, investigators observed a covert configuration hook where the system was instructed to map incoming HTTP requests for image files—specifically those ending in .ico—to hidden .sig files residing in /var/netscaler/gui/vpn/scripts/linux/. When a user or automated scanner requests an icon, the server instead executes the PHP web shell. Access logs in affected environments showed instances where GET requests resulted in 404 responses but exhibited unusually high processing times and large response sizes, indicating the hidden execution of the malicious script.
To ensure long-term persistence, the attackers modify file permissions for /bin/sh and force a system reboot of the NetScaler appliance. This ensures that their malicious configurations are loaded into memory and remain active even after service restarts. Furthermore, the malware is designed to "self-clean." If no commands are received for a period of 10 minutes, the tools automatically remove their port and lock files, effectively erasing their immediate footprint to complicate forensic analysis.
Chronology of the Escalation
The timeline of the exploitation suggests a rapid transition from targeted intelligence gathering to broad-scale criminal activity. By late September 2026, security firm GreyNoise began detecting a surge in malicious activity tied to both CVE-2026-88771 and CVE-2026-88772.
- September 28, 2026 (8:30 a.m. EDT): Initial signs of mass reconnaissance were recorded, suggesting that various threat actors were scanning the internet for unpatched Citrix appliances.
- September 28, 2026 (10:30 p.m. EDT): A significant surge in activity was observed. What began as automated scanning quickly evolved into active exploitation and the deployment of web shells.
- Late September 2026: Mandiant and Google finalized their reporting, identifying that the activity was not limited to a single actor but was being utilized by multiple, disparate groups for botnet recruitment and access brokering.
Broader Implications for Network Security
The exploitation of CVE-2026-88772 highlights a critical weakness in modern enterprise security architectures: the reliance on internet-facing edge appliances that are often neglected in standard patch cycles. Because these devices (Application Delivery Controllers, VPN gateways, and firewalls) operate at the perimeter, they represent a "blind spot" for many organizations.

"These appliances remain attractive targets because they are exposed to the internet, sit outside the reach of EDR tools, and often store or process credentials that can be used to move deeper into the network," stated representatives from Google’s cybersecurity division. The breach underscores the necessity for organizations to treat edge hardware with the same, if not higher, level of security scrutiny as end-user workstations and servers.
The potential for lateral movement is the most significant concern for security teams. By gaining root access at the edge, an attacker can theoretically intercept authentication tokens, clear-text credentials, and session cookies for any user passing through the VPN gateway. This grants the attacker the ability to impersonate legitimate users and traverse the network with the credentials of a trusted employee, making the subsequent removal of the threat actor exceptionally difficult.
Industry Response and Recommendations
The industry response has been swift, with cybersecurity agencies and the vendor issuing urgent guidance to apply the relevant security patches. For organizations utilizing Citrix NetScaler, the primary recommendation is to update all appliances to the latest patched firmware immediately.
Beyond patching, security experts suggest the following defensive measures:
- Monitor Web Server Configurations: Regularly audit
httpd.conffiles and other configuration scripts for unauthorized modifications or unexpected file associations. - Analyze Log Anomalies: Inspect web server logs for requests that result in 404 errors but show abnormal processing times or unusually large response sizes, as these may indicate hidden web shell execution.
- Implement Network Segmentation: Limit the ability of edge appliances to communicate with internal sensitive assets unless absolutely necessary, thereby reducing the impact of a lateral movement phase.
- Adopt Zero-Trust Principles: Assume the edge device is compromised and implement strict access controls and multi-factor authentication (MFA) that do not rely solely on the appliance’s internal databases.
The current situation remains fluid, with security analysts monitoring for new variations of the WHIPSHOT and SLAPSHOT tools. As of early October 2026, the primary focus for the global security community is to identify and remediate remaining vulnerable instances before they are absorbed into the growing botnets identified by GreyNoise. The event serves as a stark reminder of the persistent and evolving nature of threats targeting critical infrastructure components that underpin the digital economy. Organizations that have not yet verified the integrity of their NetScaler environments are advised to initiate a thorough forensic audit to ensure that no unauthorized persistence mechanisms have been established.
Related posts: