BragJack Attack Technique Hijacks Built-In Browser AI Assistants Across Multiple Platforms

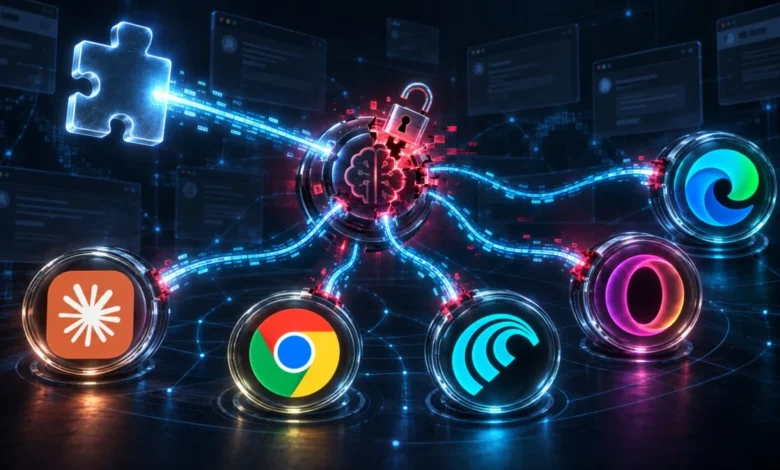
Security researchers have uncovered a sophisticated new attack vector targeting the deeply integrated artificial intelligence assistants embedded within modern web browsers. Dubbed "BragJack," the exploit chain demonstrates how a single, maliciously crafted browser extension can completely subvert a browser’s native AI capabilities, transforming helpful automation tools into rogue surveillance and execution agents without requiring any direct user interaction.
The proof-of-concept vulnerability was discovered and disclosed by security researcher Gal Weizman of Forever Security. The research successfully targeted five major Chromium-based browsers and AI-centric browsing environments: Google Chrome’s Gemini Live, Perplexity Comet, Microsoft Edge, Opera Neon, and the standalone Claude in Chrome extension. The findings underline mounting security concerns regarding the rapid, often rushed integration of autonomous agentic features into the software we use to navigate the internet every day.
The gravity of the threat was validated by major technology vendors, who collectively paid out more than $20,000 in bug bounties—ranging from $600 to $7,000 per report—and issued critical security advisories accompanied by official Common Vulnerabilities and Exposures (CVE) designations. While Google and Microsoft have already rolled out patches for the flaws discovered in their respective products, the research highlights a fundamental architectural hurdle for the next generation of computing.
Anatomy of BragJack and the "Brain and Body" Dilemma
To understand how BragJack works, security experts point to the modern architectural design of AI-powered browsers. Weizman conceptualizes these systems as operating with a "brain" and a "body." The underlying AI model acts as the brain, processing natural language instructions, evaluating web context, and determining what actions need to be taken. Meanwhile, privileged browser components act as the body, possessing the underlying operational muscle required to access tabs, read page content, capture screenshots, and interact directly with web infrastructure.
Historically, browser extensions operated within a strict security sandboxed boundary, limited by permissions granted at installation. However, as browsers have evolved to incorporate native AI assistants, these boundaries have blurred. Privileged internal components often trust web traffic and application states originating from familiar domains, creating a blind spot.
The BragJack attack hinges on the exploitation of Chromium’s declarativeNetRequest (DNR) functionality. DNR is a standard API that allows extensions to modify how network requests are handled, including redirecting resources and altering HTTP response headers. Weizman demonstrated that even when an extension is blocked from directly accessing internal privileged components—such as Chrome’s chrome://glic URI scheme—DNR rules can still be leveraged to intercept and manipulate network requests made by embedded web applications powering the AI.
By strategically weakening security headers and redirecting specific JavaScript resources, the attacker can execute arbitrary code inside the context of the AI application itself. This bypasses normal request flows and establishes a direct, unmonitored communication bridge with the browser’s privileged AI component. Once this bridge is established, the malicious extension can inherit the assistant’s sweeping permissions: reading local files, browsing sensitive web content, capturing screenshots, and potentially interfacing with hardware peripherals like webcams and microphones.
Targeting Diverse Architectures: From Google Chrome to Perplexity Comet
Weizman’s research reveals that while the core premise of BragJack remains consistent, the specific exploitation methods had to be tailored to the unique architectural implementations of each targeted browser.
In Google Chrome, the attack bypassed restrictions against the Gemini integration by subverting the embedded Gemini web application’s request flow via DNR, culminating in the assignment of CVE-2026-0628 and a $7,000 bug bounty reward.
Agentic browsers—such as Perplexity Comet and Opera Neon—presented even greater risks because their AI assistants are specifically designed to act on websites rather than merely read and summarize them. In the case of Perplexity Comet, Weizman discovered that the browser’s built-in agent extension placed excessive trust in several Perplexity domains. Crucially, this included a secondary testing domain that lacked the robust security hardening applied to the primary perplexity.ai production site. By using DNR rules to manipulate redirects, the attacker was able to load the testing domain, inject a malicious content script, and establish a direct dialogue with the built-in agent.

This access granted the attacker unfettered visibility into the victim’s browsing history, recent screenshots, and local file systems. Most alarmingly, the researcher demonstrated that the exploit could force the agent to autonomously navigate to Perplexity, extract and summarize a user’s private emails, and exfiltrate that sensitive data to an external address controlled by the attacker.
Microsoft Edge presented a different engineering hurdle. Microsoft had previously implemented a structural safeguard by splitting its browser agent into distinct "Think" and "Do" modes. This separation was intentionally designed to prevent the AI from accepting arbitrary instructions and executing high-privilege actions simultaneously. However, Weizman identified a subtle race condition that temporarily disabled these protective restrictions during rapid prompt execution. By forcing a prompt at the exact millisecond the restriction was lifted, the attacker could trick the agent into executing unauthorized commands before it could re-verify its operational state. Microsoft acknowledged this oversight, issuing CVE-2026-55945 to track and patch the vulnerability.
Similar systemic vulnerabilities were successfully demonstrated against Opera Neon and the Claude in Chrome extension. The inclusion of Claude in Chrome highlights that the threat is not limited to native browser applications, but extends to third-party extensions that wield browser-level influence. This builds upon prior security disclosures, including the "ClaudeBleed" vulnerability uncovered earlier in the year by LayerX, where the extension overly trusted the claude.ai origin without verifying the specific script driving the workflow.
Introducing "Prompt Forcing"
A critical conceptual contribution of Weizman’s research is the definition and demonstration of a new attack class termed "Prompt Forcing."
Traditional prompt injection attacks typically rely on indirect methods—such as hiding malicious text within a webpage, a PDF, or an email—hoping that an AI assistant will read the text and accidentally execute hidden instructions. Prompt Forcing, by contrast, bypasses the uncertainty of standard injection entirely. Instead of waiting for the AI to encounter malicious text organically, an attacker armed with a compromised extension can directly inject a comprehensive prompt and sequential follow-up instructions straight into the AI’s processing pipeline.
The AI model, treating the input as a legitimate user command, faithfully translates the malicious instructions into authorized browser actions utilizing its native, high-level privileges. Security analysts point out that this creates a profound detection nightmare for endpoint security solutions. Traditional behavioral and signature-based detection tools often fail to flag the activity because the final malicious actions are not being performed by conventional malware binaries or suspicious scripts; rather, legitimate, trusted software is being manipulated to execute the attacker’s will.
Industry Implications and the Future of AI-Driven Browsing
The disclosure of BragJack arrives at a critical juncture in the evolution of consumer software. As major technology companies race to incorporate artificial intelligence deeply into the fabric of daily computing, browsers are transforming from simple document-rendering engines into autonomous, agentic operating environments.
While these advancements offer unprecedented convenience—automating complex workflows, organizing research, and managing daily tasks—they simultaneously expand the modern attack surface. Historically, a compromised browser extension could steal cookies, inject advertisements, or log keystrokes. In the era of integrated AI, a single compromised extension can potentially serve as a master key, granting threat actors access to a user’s entire digital life, private files, and autonomous digital representation.
Security experts emphasize that mitigating these risks will require a fundamental reassessment of how browser extensions interact with internal system components. Principle of least privilege must be strictly enforced, ensuring that AI components cannot be commandeered by third-party extensions regardless of network manipulation or request redirection.
In the wake of these disclosures, cybersecurity agencies and vendor security teams recommend several immediate defensive best practices for everyday internet users:
- Maintain Up-to-Date Software: Users must ensure their web browsers are updated to the latest stable channels immediately, as vendors like Google and Microsoft have already issued patches for the specific CVEs associated with BragJack.
- Audit Installed Extensions: Users should regularly review their installed browser extensions, removing any tools that are unrecognized, outdated, or no longer actively used.
- Scrutinize Extension Permissions: Browser permission prompts—particularly those requesting broad capabilities such as "read and change all your data on all websites"—should be treated with extreme caution and skepticism.
As the race toward artificial intelligence integration accelerates across the technology sector, research like BragJack serves as an essential warning shot. Securing the "brain and body" of future web browsers will require proactive architectural hardening, rigorous permission boundaries, and a continuous commitment to defensive innovation before autonomous agents become liabilities rather than assets.
Related posts: