Critical Linux Kernel Vulnerability CVE-2026-98432 Exposes Servers to Remote Root Exploitation

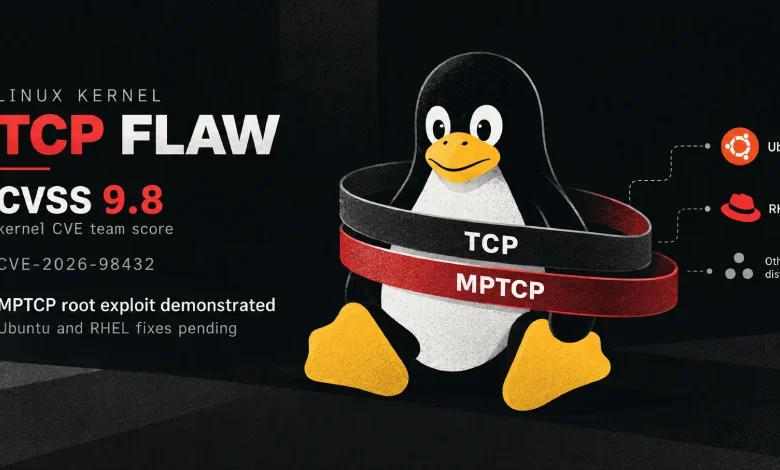
A severe security vulnerability in the Linux kernel’s TCP networking stack, cataloged as CVE-2026-98432, has sent shockwaves through the cybersecurity community. With a critical CVSS score of 9.8 assigned by the Linux kernel’s own security team, the flaw represents a significant risk to enterprise infrastructure, potentially allowing unauthenticated remote attackers to execute arbitrary code with root privileges. The vulnerability, which stems from a race condition in the handling of IPv4 TCP connection setups, has highlighted both the power of AI-assisted vulnerability research and the persistent challenges of patch management across fragmented Linux distribution ecosystems.
The core of the issue lies within the kernel’s memory management during the TCP handshake process. Specifically, when a new connection is established, the kernel fails to properly duplicate IP options stored with a pending request before passing them to the newly created socket. If a malicious actor triggers a race condition—where the socket is destroyed by one CPU core while another is still processing the IP options for a retransmitted request—the kernel engages in a "use-after-free" operation. This allows the system to read memory that has already been deallocated, a classic precursor to more sophisticated memory corruption exploits.
The Emergence of AI-Driven Threat Discovery
The discovery of this exploit has brought the role of artificial intelligence in cybersecurity to the forefront. On October 27, 2026, AI research firm Anthropic disclosed that its advanced language model, Claude, was instrumental in identifying the vulnerability and developing a functional exploit chain. According to Anthropic, the AI model required only minimal initial prompting to synthesize a two-stage attack.
In the first stage, the exploit leverages the race condition to leak kernel memory, effectively bypassing Kernel Address Space Layout Randomization (KASLR), a critical defense mechanism that masks the location of the kernel in memory. Once the KASLR protection is bypassed, the second stage involves a buffer overflow that overwrites a callback pointer with a malicious payload. Because the kernel eventually executes this pointer, the attacker is able to force the system to run arbitrary commands with root-level permissions.
The research indicates that the attack is not a "one-and-done" effort but rather a persistent one. If an attacker loses the race, the current connection simply fails, allowing the attacker to attempt the exploit repeatedly without crashing the target server. In controlled testing, Anthropic reported that the process of leaking the necessary address took approximately 48 minutes, with full command execution achieved in an additional five minutes.

Chronology of the Vulnerability
The lifecycle of CVE-2026-98432 spans from the introduction of the flawed code to the current state of industry-wide remediation:
- Initial Introduction: The bug was introduced into the Linux kernel codebase as early as version 4.4, meaning the flaw has potentially existed in various production environments for years.
- Discovery and Reporting: The vulnerability was reported to the Linux kernel maintainers by Anthropic researcher Xinyang Ge.
- Upstream Patching: The kernel development community identified and committed a fix on October 5, 2026. This patch mandates that the kernel wait for all CPU operations on the IP options to complete before freeing the associated memory.
- Public Disclosure (CVE Publication): The CVE was officially published on October 15, 2026.
- Escalated Scoring: The Linux kernel security team assigned the 9.8 CVSS score on October 24, 2026, citing the relative ease with which an attacker can force both sides of the race condition.
- Anthropic Disclosure: Anthropic released its research on October 27, confirming that the AI-assisted exploit was capable of targeting Multipath TCP (MPTCP) listeners.
- Current Status (October 29): Patch availability remains inconsistent across major Linux distributions, with enterprise-grade operating systems like Ubuntu and Red Hat Enterprise Linux (RHEL) yet to ship finalized kernels.
Discrepancies in Risk Assessment
One of the most notable aspects of CVE-2026-98432 is the significant disagreement regarding the severity of the flaw among major Linux vendors. While the Linux kernel team maintains a 9.8 "Critical" rating, others have been more conservative.
Red Hat, for instance, initially assigned the vulnerability a "Moderate" rating with a CVSS score of 5.9, arguing that the race condition is difficult to win reliably and that the most likely outcome of a failed attempt is a system crash rather than a full system compromise. However, as of October 29, internal pressure and further analysis led to an update in their security advisory, upgrading the status to "Important" with a score of 8.1.
Similarly, Oracle and SUSE have settled on an 8.1 score. The discrepancy largely centers on the "Attack Complexity" metric. The kernel team views the race as easily repeatable by an attacker, while vendors like Red Hat suggest that environmental factors and the inherent instability of the race make it less viable for widespread automated exploitation. Amazon, meanwhile, has taken a middle-ground approach, scoring the flaw at 7.0 for its affected Amazon Linux 2023 kernels.
Impact on Enterprise Distribution Ecosystems
The delay in patching highlights the "last mile" problem in Linux security. While the kernel maintainers fixed the bug at the source, individual distributions—which often backport patches to older, stable kernels—must perform their own testing to ensure stability.
As of the latest reports, Debian, Oracle Linux, SUSE, and Amazon Linux have successfully pushed updates for their supported versions. Conversely, users of Ubuntu and RHEL are currently in a "wait and see" position. Red Hat has explicitly stated that the fix has been "deferred to a future update," leaving organizations relying on RHEL to monitor for further announcements. Ubuntu has similarly characterized its patching process as "work in progress," with no concrete release date for the security update.

The situation is particularly precarious for organizations running legacy or non-standard kernel configurations, such as FIPS-compliant, real-time, or cloud-optimized kernels. These specialized distributions often require additional validation, meaning the "patch gap" for these users may persist even after the general-purpose kernels are updated.
Strategic Analysis: The Future of AI in Security
The involvement of Anthropic’s AI model in documenting this vulnerability marks a transition point in cybersecurity. Previously, the development of sophisticated kernel-level exploits was the domain of highly skilled human researchers who could spend weeks or months analyzing code. The ability of an AI to automate the discovery of such a deep, race-condition-based vulnerability signals that the "bar to entry" for offensive cyber operations is lowering.
This trend creates an asymmetric environment where developers and security maintainers are forced to play catch-up against automated tools that can analyze code faster than human teams can write and test patches. The fact that the bug was discovered and exploited by an AI before it was widely understood by the security community underscores the need for proactive, AI-driven defense mechanisms. Organizations must move toward a model of "continuous security," where code is audited for such race conditions as a matter of routine during the development lifecycle, rather than relying on reactive patching after a CVE is published.
Recommendations for System Administrators
Until a distribution-specific patch is available, administrators are advised to monitor official security channels from their respective vendors. While no specific "silver bullet" mitigation has been released, experts suggest that limiting exposure to untrusted networks and monitoring for unusual TCP handshake patterns can provide a temporary layer of defense.
For those managing custom-built kernels, the recommendation is clear: update to the latest stable release. The official fix is included in the following kernel versions: 5.10.272, 5.15.223, 6.1.190, 6.6.159, 6.12.113, 6.18.56, 7.2.10, and 7.3. The Linux kernel security team explicitly warns against "cherry-picking" individual fixes, as the complex nature of the TCP stack means that partial implementation could leave other vulnerabilities open or lead to system instability.
As the industry continues to navigate the implications of CVE-2026-98432, the event serves as a stark reminder of the complexity of the Linux kernel. It is a shared infrastructure upon which the vast majority of the modern digital economy is built, and its security remains a collective responsibility that requires both human diligence and the integration of emerging technologies to maintain. Whether through faster patch deployment or more robust, memory-safe coding practices, the response to this vulnerability will likely shape how Linux vendors approach kernel security in the years to come.
Related posts: