Google and Industry Partners Dismantle Massive XCPE Botnet Infecting Over 1.3 Million Android TV Devices

In a significant collaborative strike against global cybercriminal infrastructure, Google, working alongside international security partners, has successfully dismantled the XCPE botnet, a sophisticated network of more than 1.3 million compromised Android TV set-top boxes. The operation, which marks a major milestone in the fight against Internet of Things (IoT) exploitation, has severed the command-and-control infrastructure used to turn consumer electronics into unwitting tools for advertising fraud and malicious traffic routing. Cybersecurity experts warn that while the primary botnet is offline, the reach of the underlying infection vector may extend to more than 10 million additional devices, including specialized hardware such as telehealth monitors, karaoke machines, and digital signage systems.
The investigation, spearheaded by the Google Threat Intelligence Group (GTIG), revealed that the primary source of the infection was the Chinese manufacturer Videostrong Technology Co. The firm systematically embedded malicious firmware into their products at the factory level. This "backdoored" software, dubbed XCPE after one of its core code components, was designed to activate immediately upon the device’s first boot, effectively turning millions of unsuspecting living rooms into nodes for a global "residential proxy" network.
The Anatomy of the XCPE Botnet
The core business model of the XCPE botnet was the monetization of residential internet bandwidth. By installing malware on these Android-based TV boxes, the operators were able to hijack the user’s home network connection. This bandwidth was then sold to third-party "residential proxy" services. These services are frequently utilized by legitimate businesses for web scraping or market research, but they are also highly sought after by criminal syndicates.
When a device is enslaved by a residential proxy service, its IP address acts as a gateway for external traffic. Because this traffic appears to originate from a legitimate home connection, it is incredibly difficult for security filters to block. Consequently, these hijacked devices were used to facilitate account takeover attacks, bypass regional content restrictions, execute large-scale advertising fraud, and scrape sensitive data for unauthorized AI training projects.
GTIG’s analysis confirms that Videostrong did not merely infect devices for their own gain; they actively sold access to the backdoor to other criminal affiliates. These third parties were then able to push additional, more invasive malware modules onto the already compromised hardware, creating a multi-layered ecosystem of exploitation that prioritized profit over the security and privacy of the end-user.

Chronology of Discovery and Takedown
The collapse of the XCPE botnet is the culmination of a year-long investigation involving multiple cybersecurity firms, including Synthient, and coordinated legal action by Google. The timeline of this operation reveals a sophisticated cat-and-mouse game between threat actors and security researchers:
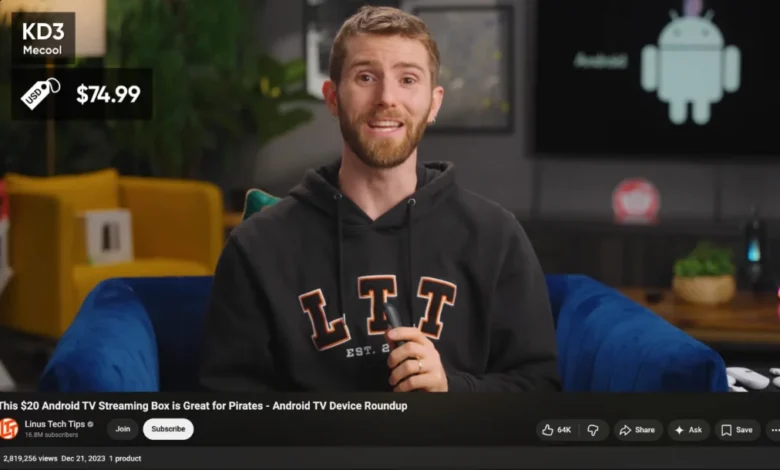
- Early 2023: MECOOL brand devices, manufactured by Skyworth Technology and utilizing Videostrong components, see a surge in popularity following endorsements from prominent tech influencers, including the YouTube channel Linus Tech Tips.
- January 2026: Synthient releases research on the Kimwolf botnet, highlighting how it exploited residential proxy vulnerabilities to hammer global networks with record-breaking Distributed Denial of Service (DDoS) attacks.
- June/July 2026: The FBI and industry partners act to seize hundreds of domains linked to NetNut, a residential proxy operator linked to the "Popa" botnet, which also utilized compromised TV boxes.
- November 2026: Google officially announces the takedown of the XCPE botnet. Legal action is taken against the domains and servers used by Videostrong to manage the malware installation and communication.
- Post-Publication (November 2026): Proxy providers, including those under the "Source" umbrella (formerly Oxylabs/Honeygain), issue statements regarding their internal audits and the suspension of suppliers linked to the malicious activity.
The Role of the Residential Proxy Ecosystem
The investigation has placed a spotlight on the residential proxy industry, which has faced increasing scrutiny for its lack of oversight. Many of the companies named in the GTIG report—including AppSalt (Honeygain), NetNut, EarnFM, Traffmonetizer, and others—provide Software Development Kits (SDKs) that allow users to "rent out" their bandwidth in exchange for small payments.
However, the XCPE case demonstrates that these SDKs are being weaponized without the user’s knowledge. The manufacturers, such as Videostrong and potentially others, pre-loaded these SDKs into the device firmware, ensuring that the device would begin functioning as a proxy node the moment it was connected to the internet.
In response to the findings, Oxylabs, now part of the Source entity, stated that their systems are designed to operate only with explicit user consent. They alleged that developers of the malicious software were "faking" the consent signals to bypass their internal verification processes. "We have been conducting regular audits of the applications provided by our partners," the company noted in a statement. "However, following this incident, we will improve the application and application’s build fingerprinting logic to better detect cases where the SDK is running on an unapproved build."
Wider Implications for IoT Security
The infection of TV boxes, telehealth devices, and digital signage represents a systemic failure in the current IoT supply chain. Unlike traditional computers or smartphones, which receive regular security updates and are often protected by robust endpoint security software, many IoT devices are "set and forget." Users rarely check for firmware updates, and manufacturers often treat security as an afterthought to reduce production costs.
Google has noted that it mandates strict security and compatibility testing for all Android device manufacturers. However, the discovery of the XCPE malware—which loaded immediately upon boot—suggests that manufacturers were finding ways to bypass these checks after the devices had left the factory or through unauthorized modifications to the system partition.

The implications of this breach are severe. By gaining a foothold in the home network, these devices effectively bypassed firewalls and security routers. Because the malware lived inside the TV box, it could potentially scan for and compromise other devices on the same local network, such as personal laptops, smart home hubs, or security cameras.
Moving Toward a More Secure IoT Landscape
The dismantling of the XCPE botnet is a significant victory, but experts warn it is only a partial solution. The sheer number of affected devices and the modular nature of the malware mean that other, similar botnets likely remain active.
For the average consumer, the advice from security professionals is increasingly urgent:
- Network Segmentation: Whenever possible, place IoT devices on a separate "guest" Wi-Fi network. This prevents compromised devices from accessing more sensitive hardware on your primary network.
- Brand Awareness: Be wary of "budget" streaming boxes that promise access to premium content for a one-time, low fee. These devices are the primary targets for pre-installed malware.
- Firmware Vigilance: If a device is still supported by its manufacturer, ensure it is updated to the latest available firmware. If a device has not received an update in years, it should be considered a security liability and retired.
The collaboration between Google, the Motion Picture Association, and research firms like Synthient serves as a new model for handling large-scale infrastructure threats. By targeting the financial and technical underpinnings—the domains, the servers, and the distribution chains—rather than just the individual infected nodes, the security community has shown that it can effectively disrupt even the most entrenched criminal operations.
As the industry moves forward, the focus must shift toward mandatory transparency for IoT manufacturers. If a device is to be connected to the internet, consumers deserve to know what software is running on it and what data is being shared. The XCPE incident is a stark reminder that in an increasingly connected world, the weakest link in the chain—often a low-cost, unmonitored streaming box—can compromise the security of the entire network. The task now lies in holding manufacturers accountable and ensuring that the devices powering our modern homes are built with security as a foundation, rather than an optional add-on.