AWS Continuum for Code Vulnerabilities Launches to Automate and Validate Cloud Security Patching

The landscape of software security has reached a critical inflection point where the velocity of cyberthreats routinely outpaces human response capabilities. Malicious actors, increasingly empowered by frontier artificial intelligence models, can now transform newly disclosed vulnerabilities into active exploit code within a matter of minutes. In response to this escalating threat paradigm, Amazon Web Services has announced the official general availability of AWS Continuum for code vulnerabilities. This advanced security service is engineered to fundamentally transform how organizations identify, validate, prioritize, and remediate application security flaws. By combining automated verification, contextual environment mapping, and intelligent patch generation, AWS Continuum aims to alleviate the overwhelming operational burdens currently facing modern software development and security teams.
The Modern Vulnerability Management Crisis
To understand the necessity of a service like AWS Continuum, one must examine the current state of application security within enterprise environments. Modern software ecosystems are vast, interconnected, and constantly evolving. Organizations running large application estates rely heavily on automated security scanners—such as static application security testing (SAST) and software composition analysis (SCA) tools—to detect potential weaknesses. However, these traditional scanners often generate thousands of alerts every single day.
A significant percentage of these findings represent "noise" rather than actionable risk. Many alerts highlight vulnerabilities that are unreachable via network paths, entirely unexploitable within the specific runtime context, or already effectively mitigated by existing runtime controls and web application firewalls. Furthermore, generic severity scoring systems frequently fail to account for the unique topology of an organization’s infrastructure. Consequently, a vulnerability marked with a critical severity score on an isolated, development-only utility can appear identical to a medium-severity flaw residing on a service situated just one network hop away from a core financial database.
Historically, determining whether a specific vulnerability posed a genuine, exploitable threat required hours or even days of tedious manual investigation by senior security engineers. Once confirmed, shipping a patch demanded extensive cross-functional coordination between security operations, infrastructure engineering, and application development teams. Because assessing the blast radius of a code change without deep business context is exceptionally difficult, deployments were frequently delayed, leaving organizations exposed to rapidly moving threat actors. AWS Continuum has been engineered to bridge this critical gap by providing empirical proof of exploitability and bounding the risk associated with every proposed remediation.
How AWS Continuum Operates: Context Graphs and Sandbox Validation
The core innovation of AWS Continuum lies in its ability to synthesize data from multiple disparate sources to build a comprehensive, real-time context graph. This graph is constructed primarily from two foundational inputs: the organization’s code repositories and its live AWS cloud environment.

To incorporate infrastructure context, administrators deploy a lightweight AWS Continuum collector within the specific AWS account and Region where applications are hosted. This collector gathers detailed resource metadata, including configurations from AWS Config and complex network topology details. By ingesting this data, Continuum gains a granular understanding of how services depend upon one another, which systems handle sensitive data such as customer records and payment pipelines, and which network pathways are exposed to potential attackers. This architectural awareness allows the service to identify an organization’s highest-value assets and accurately rank security findings based on the proximity of potential attack paths to those critical systems.
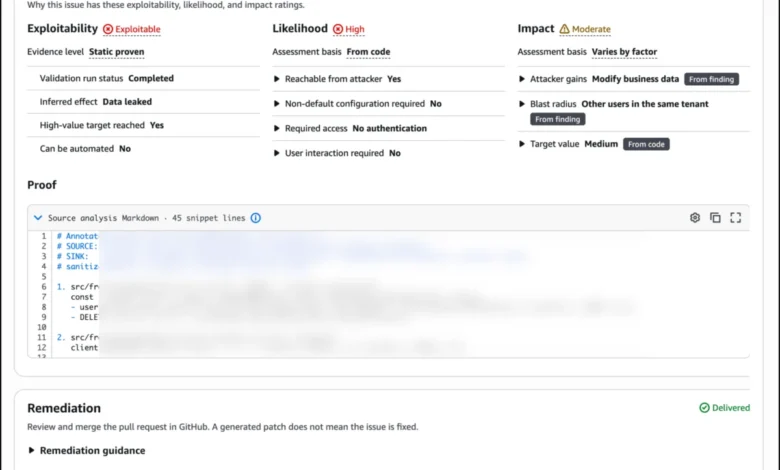
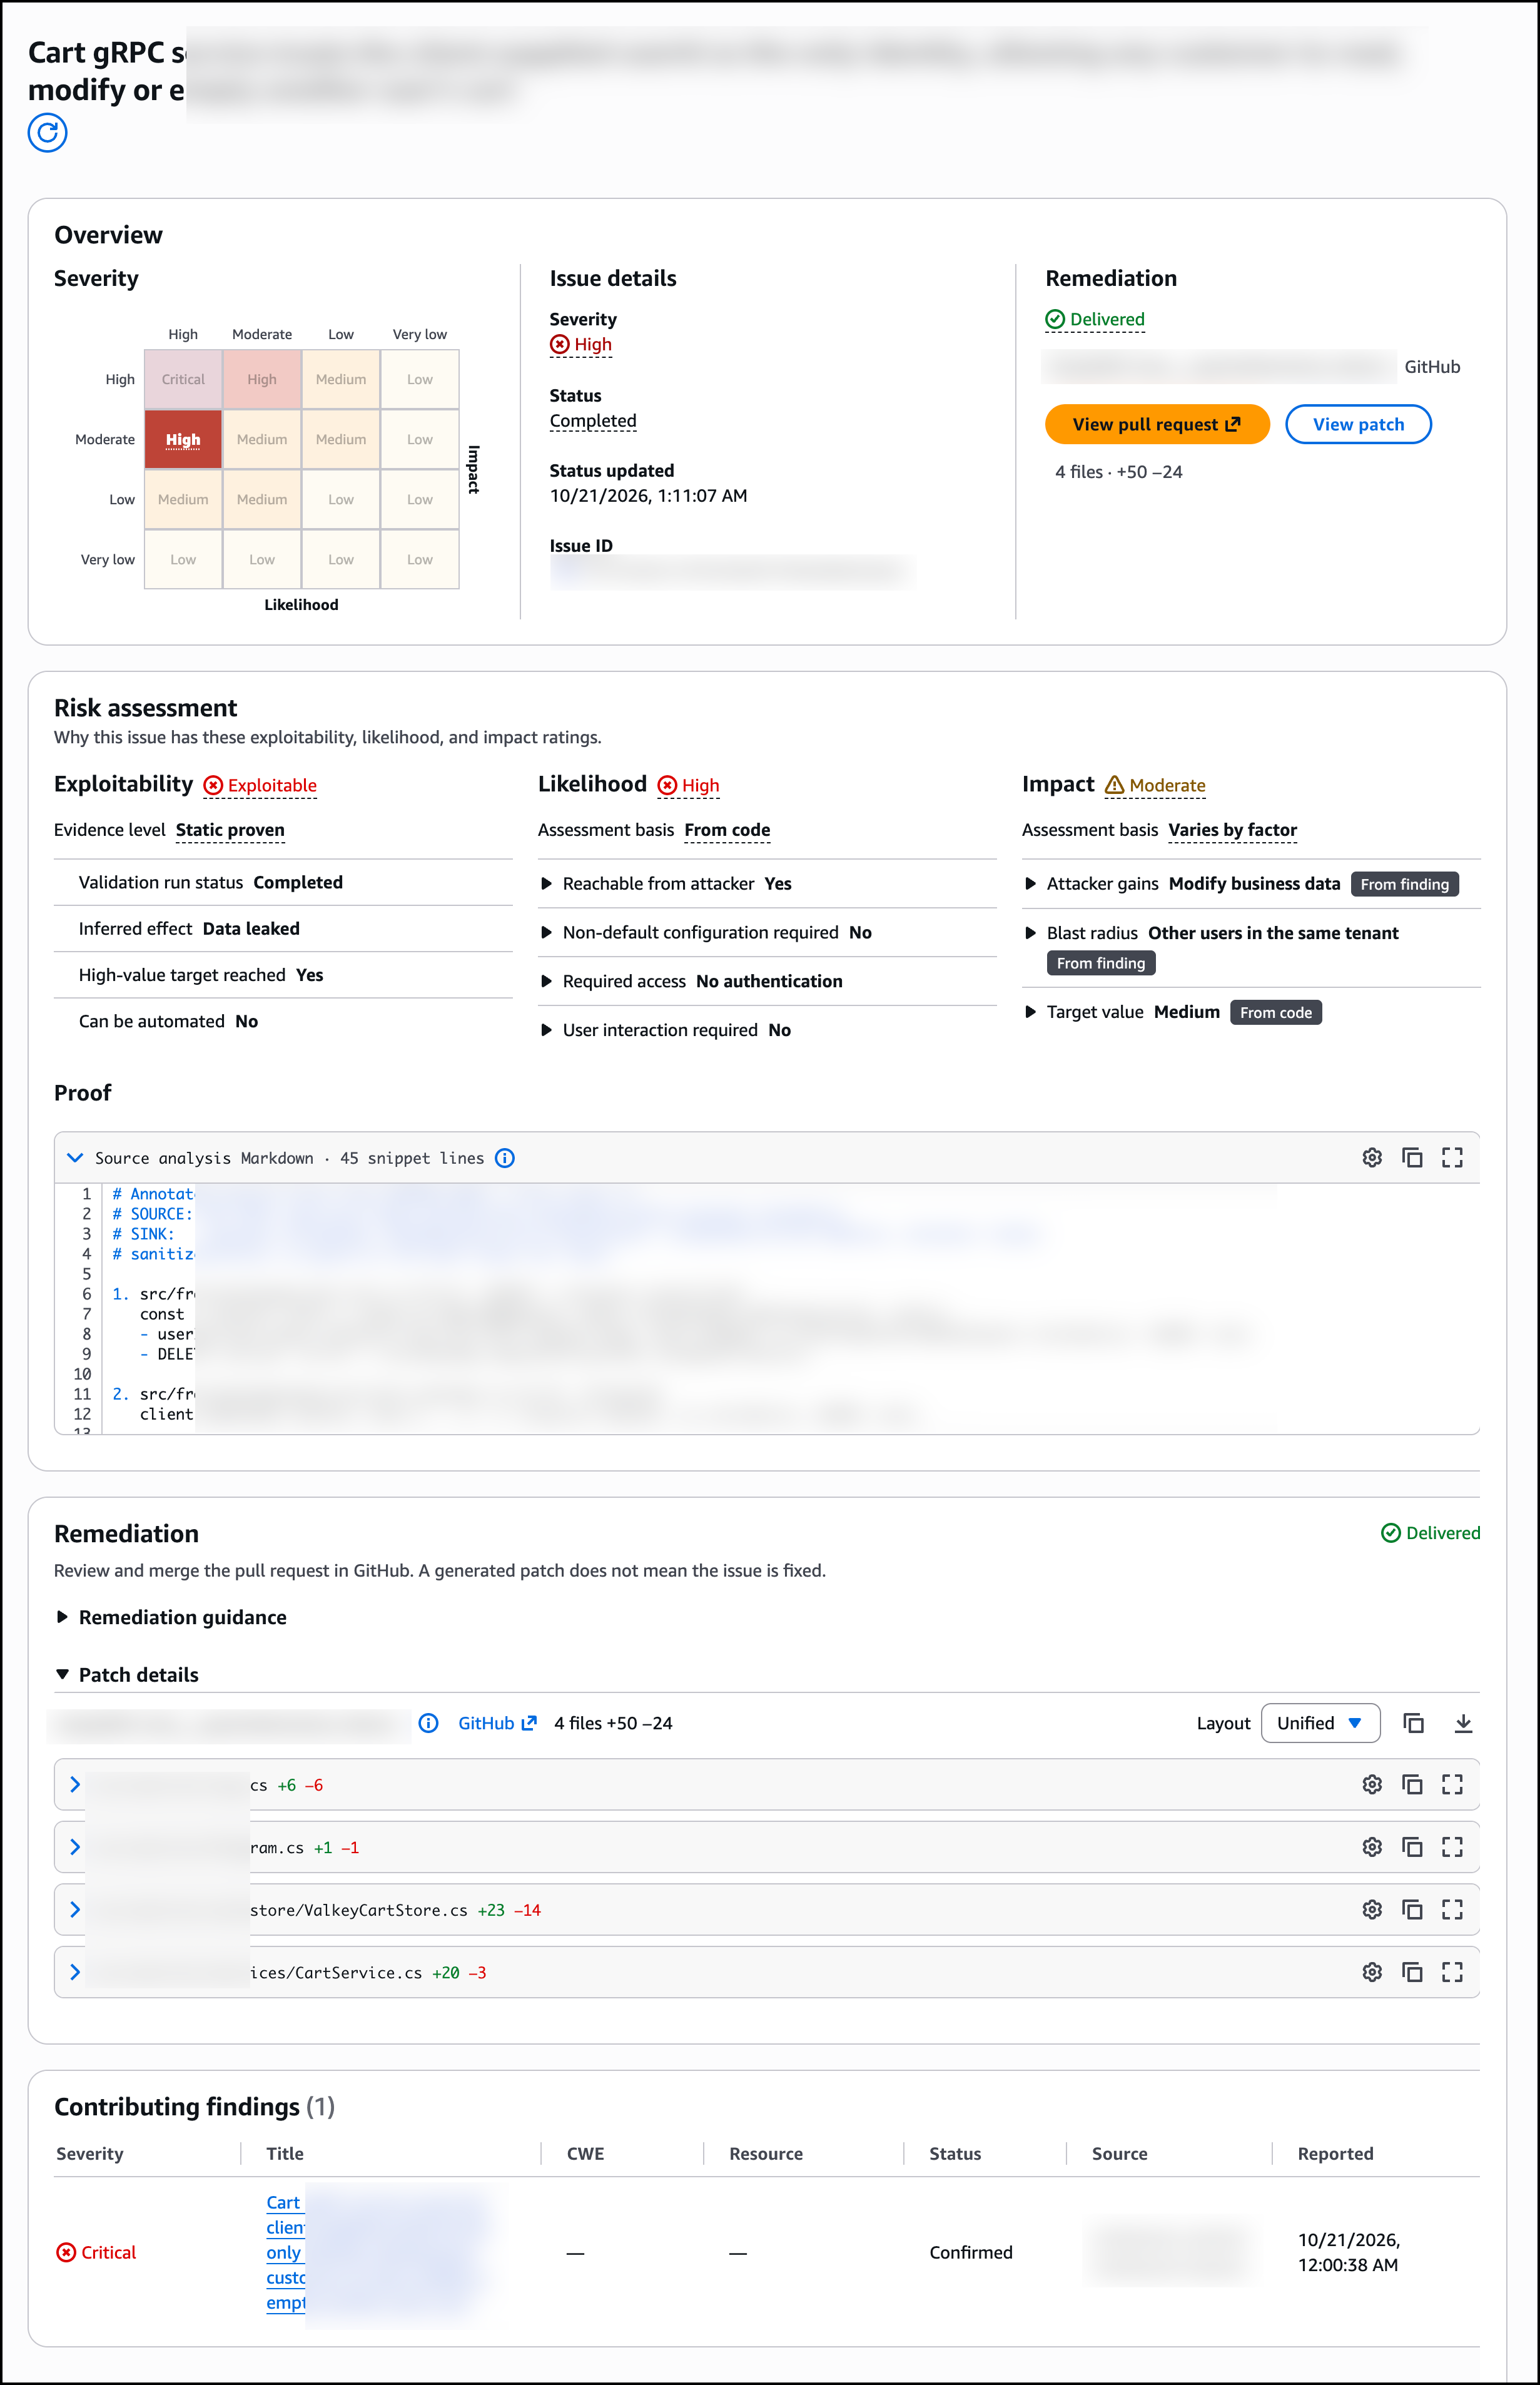
Rather than relying solely on static heuristics, AWS Continuum subjects findings to rigorous empirical validation. When a vulnerability is flagged, the service analyzes the code path alongside the environment context to assign a specific evidence level. If a finding can be actively reproduced, Continuum safely executes the exploit within an isolated sandbox environment. It then generates definitive proof-of-concept code, complete with exact reproduction steps, detailed source analysis, and a comprehensive blast radius assessment. Additionally, the service evaluates whether the organization’s pre-existing security controls would successfully detect and intercept the validated attack vector.
Automated Remediation and Human-in-the-Loop Governance
Identifying and proving a vulnerability is only half the battle; remediating it safely and efficiently is often the more complex operational hurdle. AWS Continuum addresses this challenge by automatically generating targeted fixes—such as code patches, dependency upgrades, or infrastructure configuration changes—for each confirmed issue.
These proposed fixes are delivered directly to the organization’s connected code repositories as fully formed pull requests. To maintain rigorous governance and ensure that engineering teams retain absolute authority over their codebases, every remediation initially operates under a strict human-in-the-loop model. A designated engineer must review, approve, and merge the pull request before any change is introduced to the production environment.
The integration is designed to fit seamlessly into existing developer workflows. When an engineer opens the pull request in a platform like GitHub, the description automatically populates with the complete risk assessment, remediation summary, and proof-of-concept documentation generated by Continuum. This ensures that reviewers can evaluate the evidence and understand the scope of the change without being forced to switch between disparate security dashboards and version control systems.
Looking toward the future, AWS has outlined plans to introduce configurable automation guardrails. As organizations build trust in specific remediation classes, they will soon be able to configure Continuum to apply verified patches automatically, provided the fixes pass strict predefined thresholds such as adequate test coverage, strict scope bounds, and historical success rates.
Deployment Workflow and System Requirements
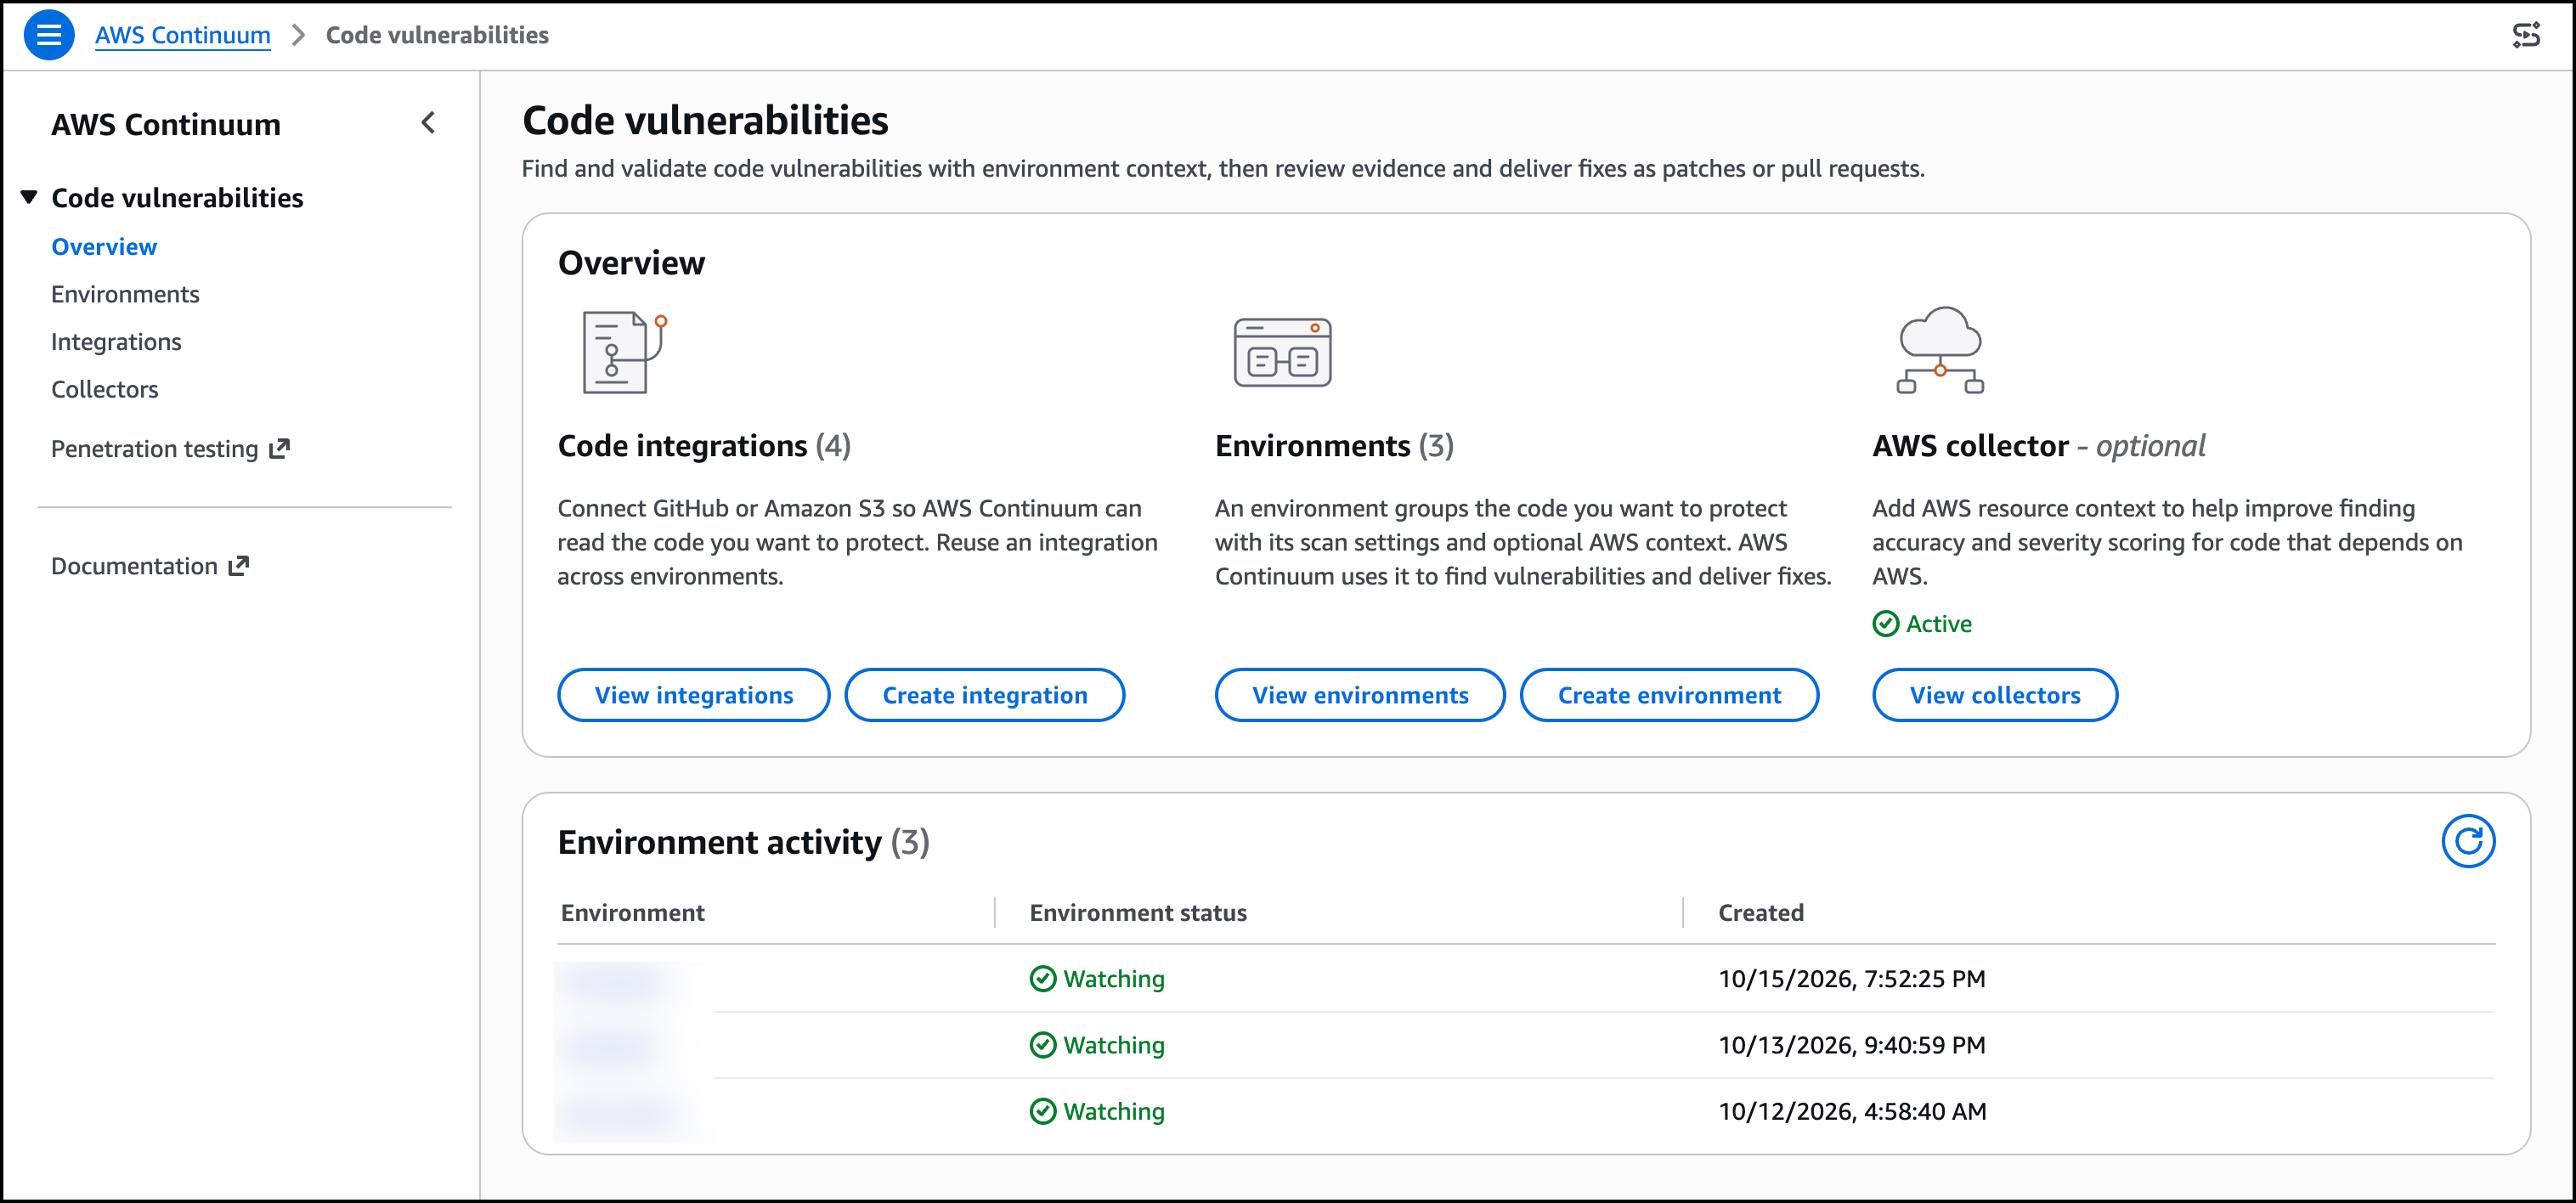
Getting started with AWS Continuum for code vulnerabilities involves a straightforward configuration process through the AWS Management Console. Administrators begin by navigating to the Code vulnerabilities section of the Continuum console and establishing an environment.
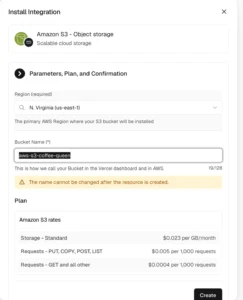
The setup process requires connecting a designated code source, which can be achieved via a direct GitHub integration or by linking an Amazon S3 bucket. Utilizing an S3 bucket as a code source involves specific prerequisites: the bucket must reside in the exact same AWS account and Region where AWS Continuum is enabled, and access must be explicitly granted through an AWS Identity and Access Management (IAM) role assumed by the service.
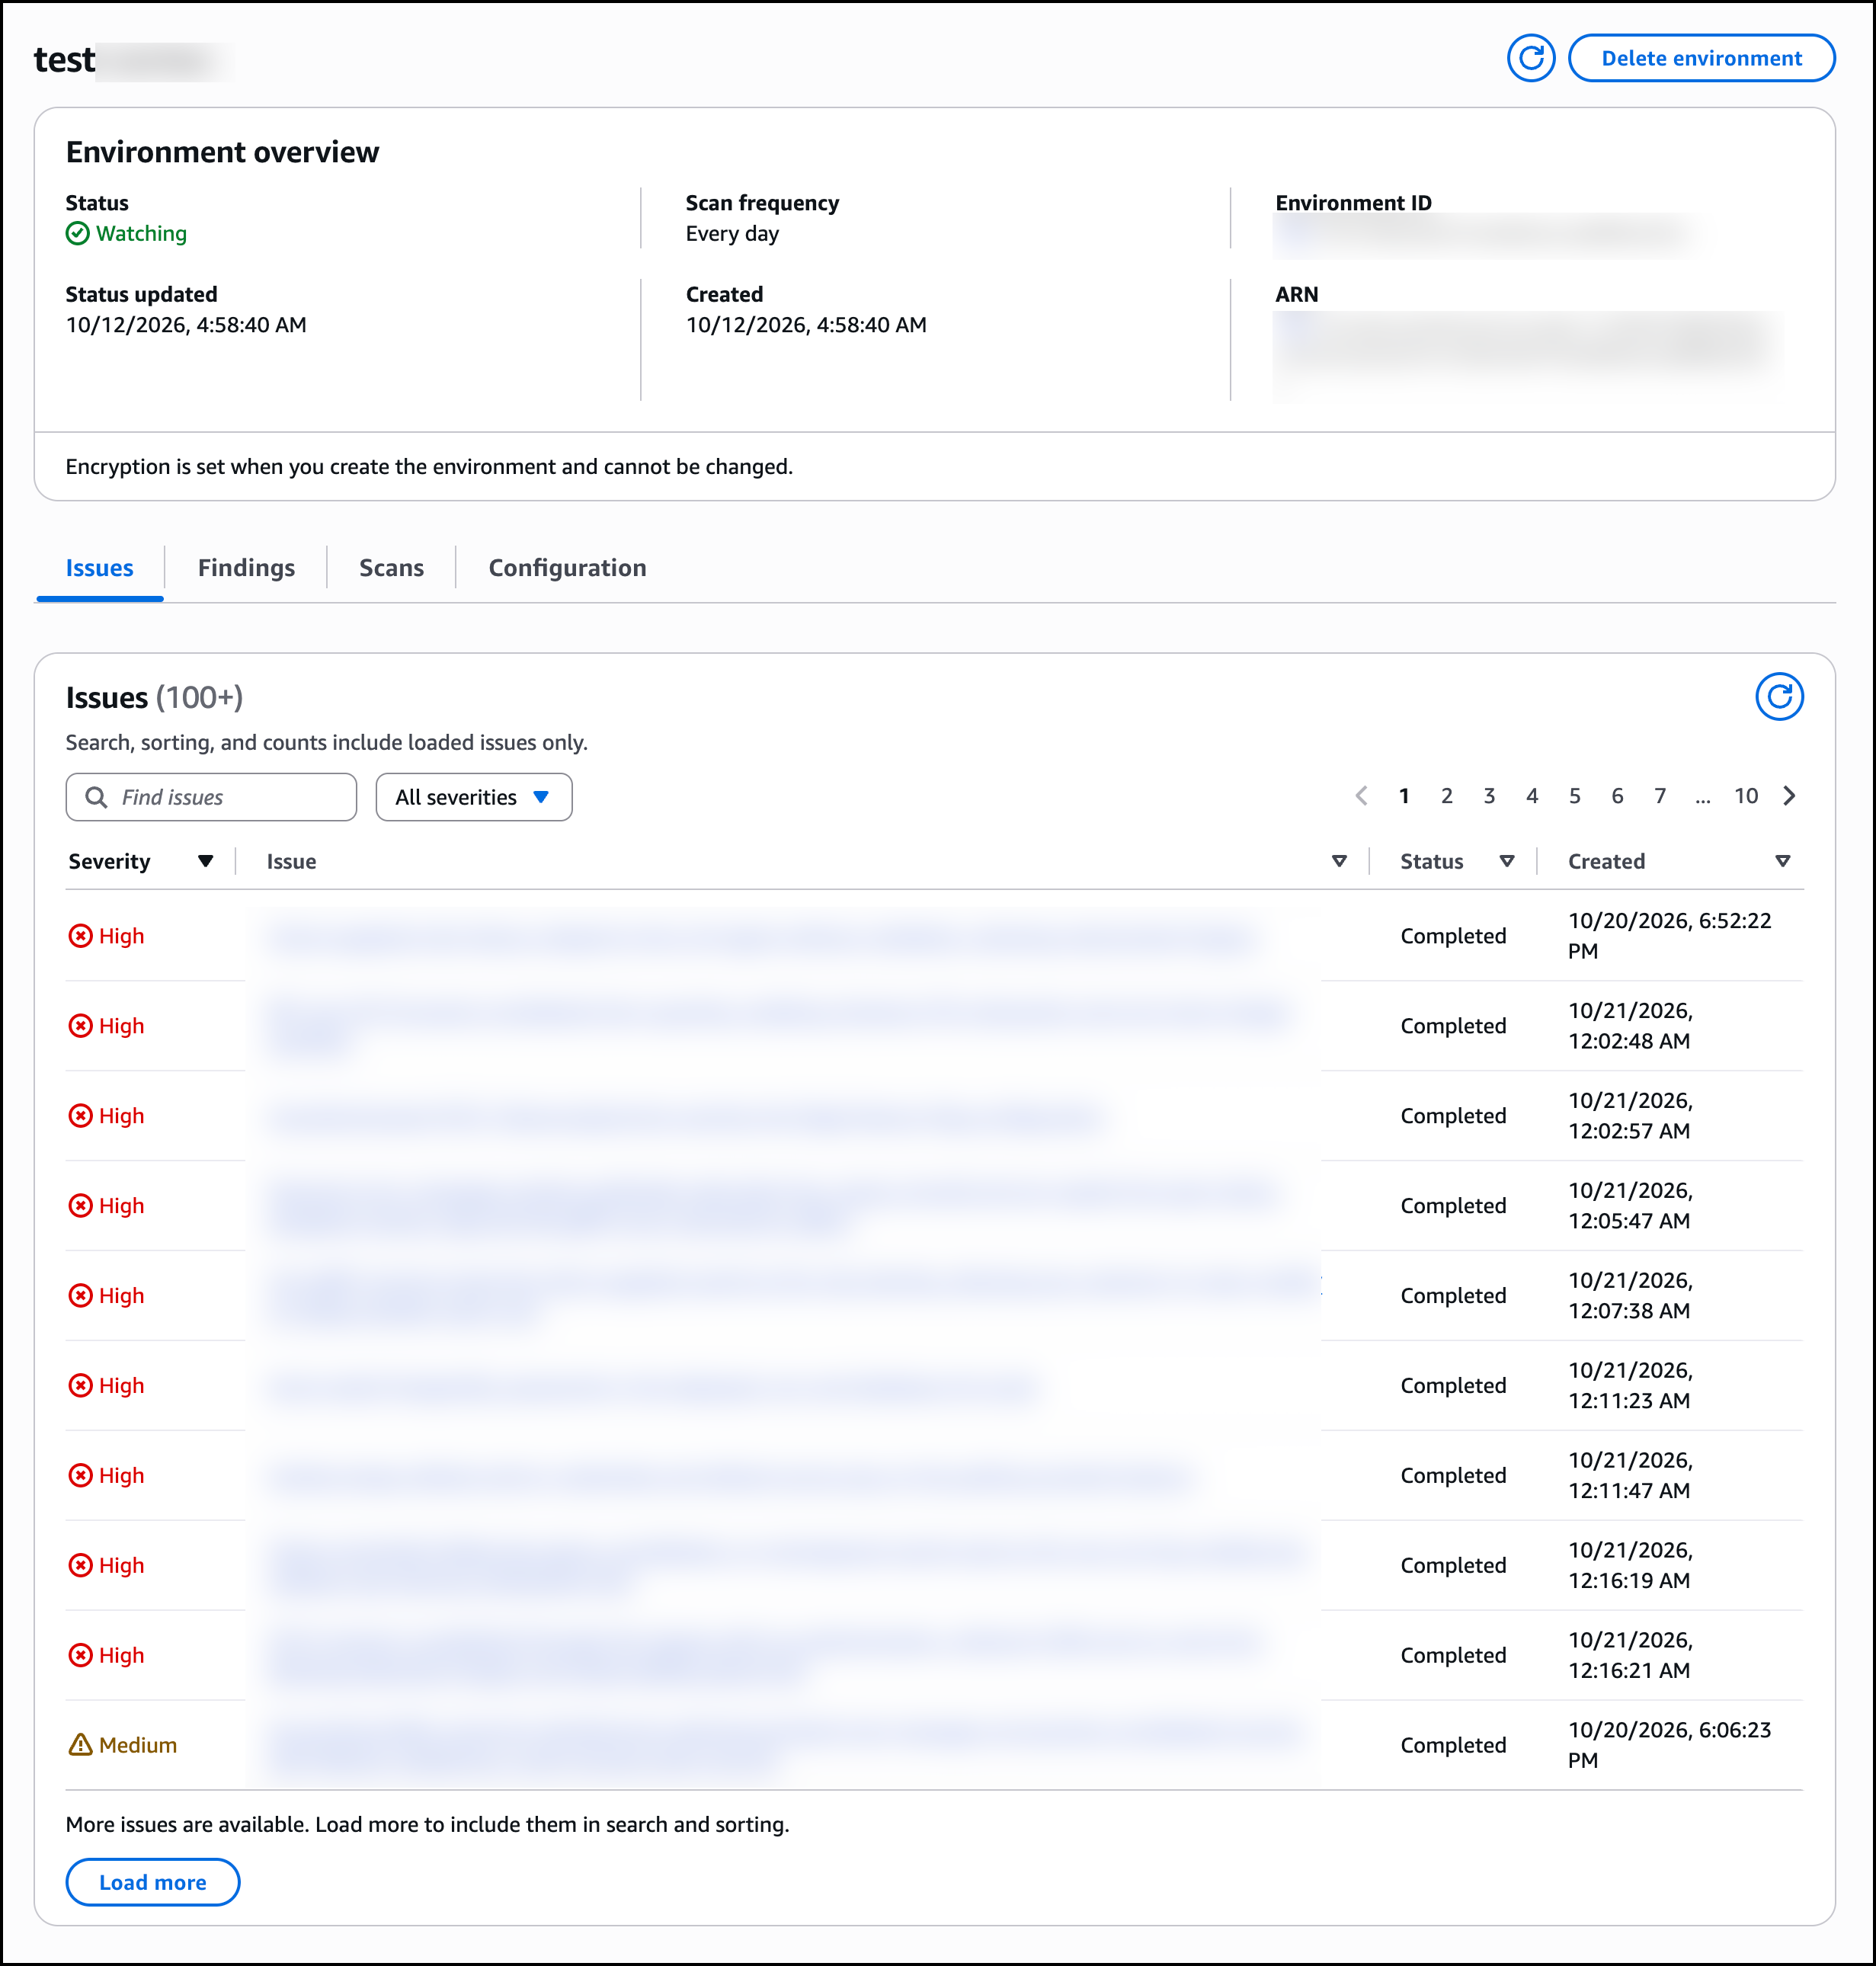
To unlock the full analytical power of the service, administrators can optionally deploy an AWS Continuum collector to supply live infrastructure context. Once the environment is configured and scheduled scans are initiated, the centralized Overview page provides a unified dashboard displaying active code integrations, environment statuses, and the health of connected AWS collectors. From the Issues tab, security personnel can review validated, prioritized findings, examine detailed risk assessments, and monitor the delivery status of automated pull requests.
Initial Availability and Regional Rollout
At the time of launch, AWS Continuum for code vulnerabilities is immediately available in select cloud regions, specifically including US East (N. Virginia) and US West (Oregon). Organizations interested in deploying the service can review detailed pricing structures on the official AWS Continuum pricing page and consult the comprehensive User Guide for step-by-step deployment instructions and technical prerequisites.
Industry Implications and Broader Impact
The introduction of AWS Continuum marks a significant evolution in cloud-native application security posture management (ASPM) and vulnerability remediation. For years, the cybersecurity industry has struggled with alert fatigue, where security teams are inundated with theoretical risks while genuine threats languish in massive backlogs. By merging static code analysis with dynamic sandbox validation and cloud environment topology mapping, AWS is shifting the industry standard from passive vulnerability reporting to active, context-aware remediation.
For enterprise organizations operating complex microservices architectures, the ability to automatically generate verified, low-risk patches promises to dramatically reduce Mean Time to Remediation (MTTR). By automating the heavy lifting of exploit verification and patch drafting—while preserving mandatory human oversight for final deployment—AWS Continuum offers a sustainable path forward in an era where application security teams must scale to meet the relentless acceleration of modern software development.